The HTML srcdoc attribute
The HTML srcdoc attribute holds the HTML that an <iframe> displays, as in srcdoc="<p>Hello</p>". Double quotes and ampersands inside the value must be escaped. The frame's document gets the address about:srcdoc, and srcdoc wins when src is set too.
Overview
The HTML srcdoc attribute gives an <iframe> its content as a string of HTML. The browser builds a whole document from that string, so a frame can show a preview, a widget or an email body without a separate file or URL.
A srcdoc value needs only body content, since the doctype and the html, head and body tags are optional. A normal page without a doctype falls into quirks mode, the old rendering mode, but srcdoc documents are exempt. A value of <p>Hi</p> produces a complete page.
A srcdoc document always has the address about:srcdoc, the same name Chrome's console uses for the frame. Relative links inside it resolve against the parent page's base URL, not against about:srcdoc. It also runs under the parent page's Content Security Policy.
Without a sandbox attribute, a srcdoc frame shares its parent's origin, which gives its scripts complete access to the parent page. A bare sandbox attribute blocks those scripts. With sandbox="allow-scripts", they run but get a SecurityError when they reach for the parent.
Syntax
<iframe title="Order preview" sandbox
srcdoc="<p>Order <b>#1024</b> ships "today".</p>"></iframe>Values
| Value |
|---|
| A string of HTML. |
Example
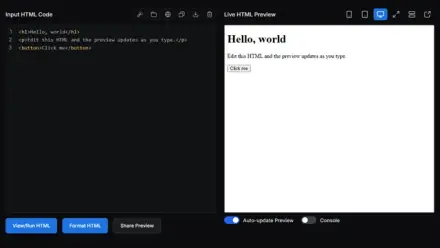
<label for="code">HTML to preview (scripts won't run)</label><br>
<textarea id="code" rows="3" cols="38"><h2>Hello</h2>
<p>This came from srcdoc.</p></textarea><br>
<button id="show">Preview</button>
<iframe id="frame" title="HTML preview" sandbox height="110" srcdoc="<p>Press Preview to load the HTML.</p>"></iframe>
<script>
document.getElementById('show').addEventListener('click', function () {
  document.getElementById('frame').srcdoc = document.getElementById('code').value;
});
</script>
Best practices
- Add
sandboxto every srcdoc frame that shows HTML you didn't write, and leave outallow-same-origin. Escaping keeps the markup inside the attribute but doesn't disarm it, since the browser decodes the attribute before building the frame. - Set markup from JavaScript through the
iframe.srcdocproperty. The property takes raw HTML, so you skip the quote and ampersand escaping that the attribute needs. - When you write the attribute by hand or on the server, turn each
&into&first and each"into"second. Done in that order, each quote ends up as", not&quot;. - Inside the frame, link to
about:srcdoc#endrather than#endwhen a link should jump within the framed page, since#endresolves against the parent page's base URL.
Accessibility
Label every srcdoc frame with a title that describes what it holds. People using assistive technology can use the title to identify an iframe, so a title such as "Order preview" helps more than "Frame" or "Preview 2".
Frequently asked questions
What is about:srcdoc?
What is the difference between srcdoc and src on an iframe?
How do I escape quotes inside srcdoc?
" and each ampersand as &. An ampersand that the framed HTML itself escapes as & therefore becomes &amp; in the attribute.Is srcdoc safe for HTML that users submit?
Why does Chrome block scripts in about:srcdoc?
Blocked script execution in 'about:srcdoc', and the parent page's script-src policy can block the frame's scripts too.